The new and improved Sandstorm App Market
By Jacob Weisz - 30 Oct 2026
We have launched a new version of the Sandstorm App Market at apps.sandstorm.org and we recommend updating your server to use it. (If you’ve already moved to our new builds of Sandstorm, we will do this for you in an upcoming release.)
Massive appreciation goes to Michael Nutt for tackling a project in a couple weeks that I wasn’t expecting to complete before 2027.
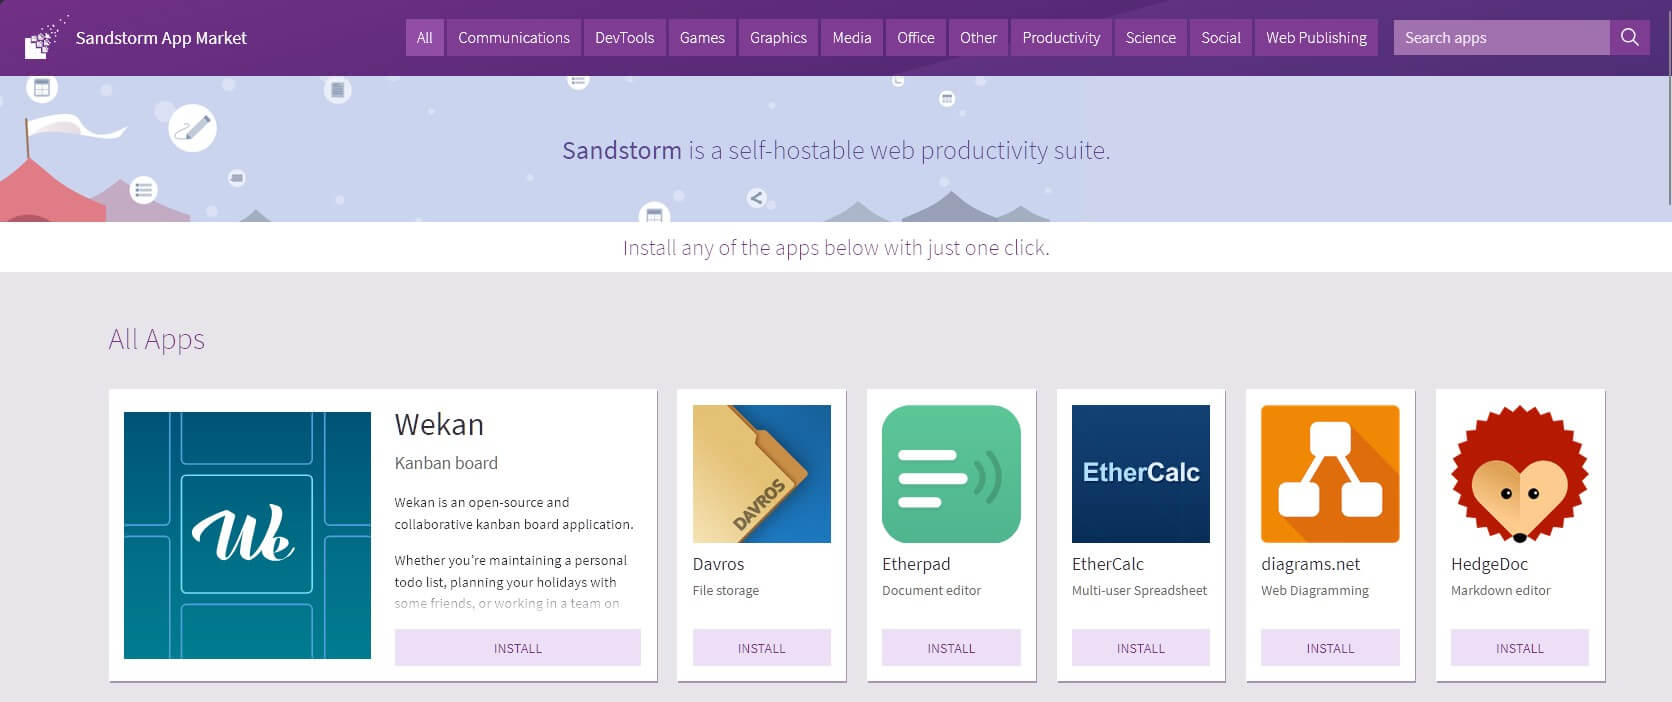
It… looks a lot like the old market. We’re excited to talk about the differences though, because the major improvements happened under the hood. The biggest visible change is that you can now see an app’s changelog right on the app page.
Underneath, however, the new app market is entirely new. The previous architecture involved two components, an app index written in C++ which is part of the Sandstorm codebase, and lives on a Sandstorm server, and the app market itself, a Meteor app which did not run inside Sandstorm but operated as a replacement front end for a Sandstorm install. The App Market used to have a system for users to post reviews, but today it lives as a static site which is generated from the app index.
The new version of the app is a single unified Sandstorm app, written in Rust, which publishes both the market interface and the app index using static web publishing. It is a fully-compatible drop-in replacement. It is open source, and we expect to publish the app in the app market itself, so you can operate your own separate app index without having to build it yourself.
New app review interface
The biggest changes lie on the administrative side of the application. The old app index printed all of the package metadata for apps in the review queue in a single long-running list. There was no sorting or navigation, and no way to look at existing published packages. All metadata from full changelogs to base64-encoded PGP keyrings simply print in a single pane that could get so long, navigation was only possible using Ctrl-F in the browser.
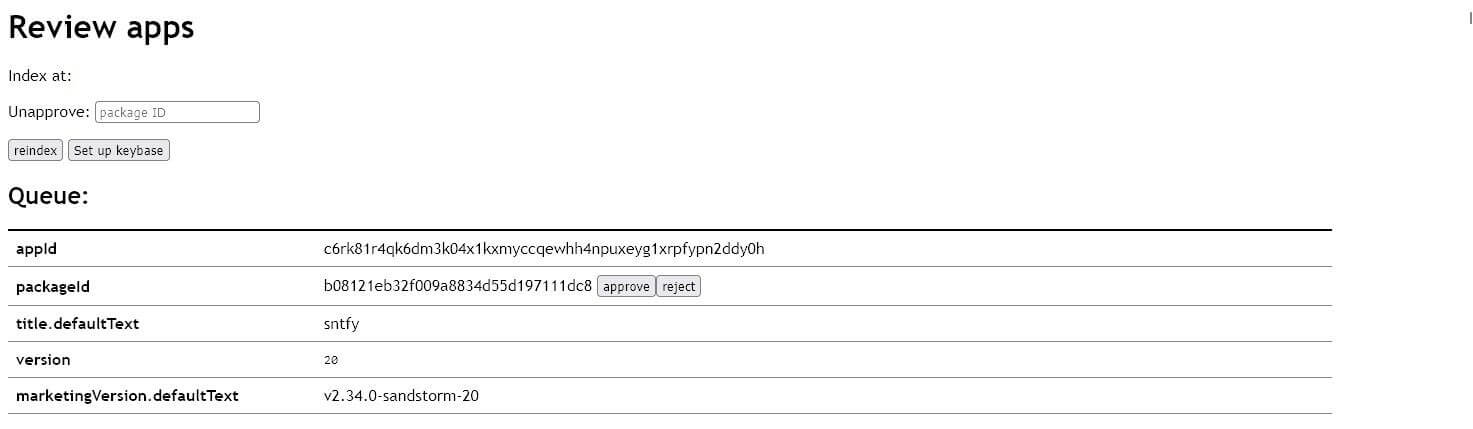
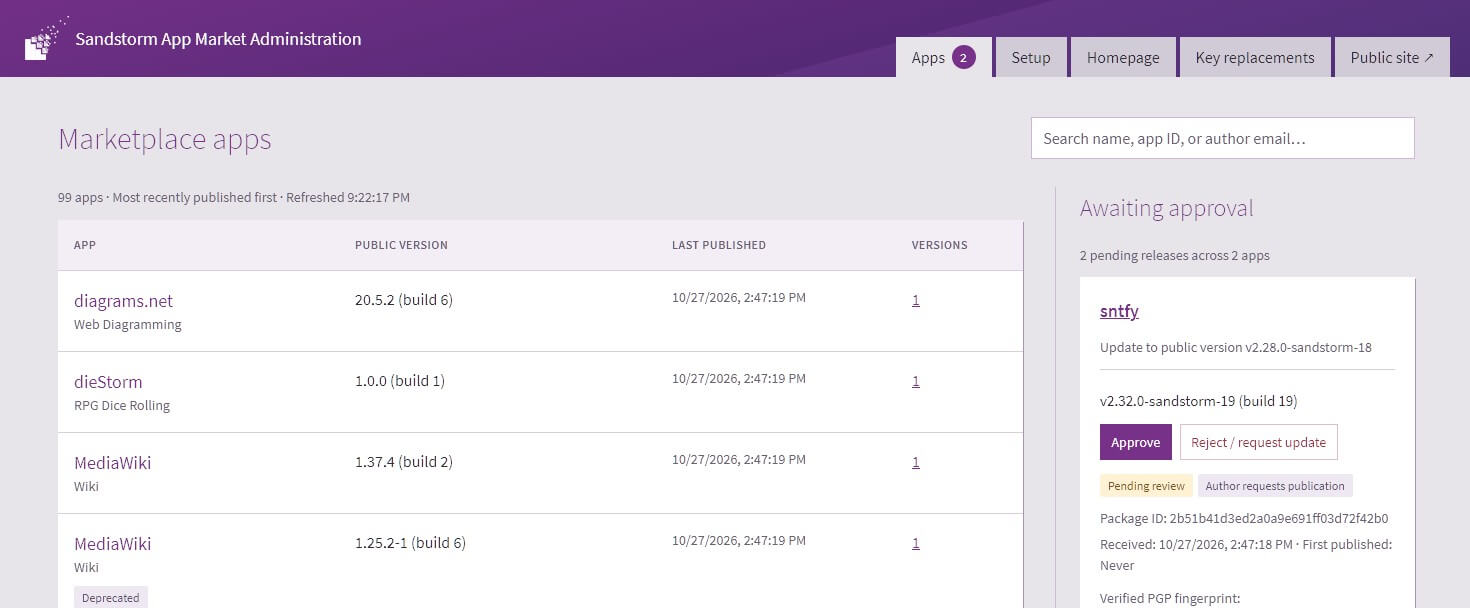
In comparison, the new app market provides a clean navigation interface allowing access to the entire package history of every package published to it. Actions are auditable and settings for notifications and pinned apps are available directly in one unified settings panel.
Handling deprecated apps
If you noticed two MediaWiki listings in the screenshot above, you have discovered the other big thing the new market handles better! We can now deprecate apps that you should not install without making them inaccessible in the case you need to restore a grain that depends on them.
Occasionally a package author decides to fully break compatibility when repackaging an existing app. This often occurs when a package is rebuilt after a very long time, and the upstream app does not handle migrations across that timespan well. We do not want to ever publish an app update which loses your data, so if the upgrade is not compatible, it must be published as a separate app.
The new app market can now mark apps as deprecated, and recommend a replacement application.
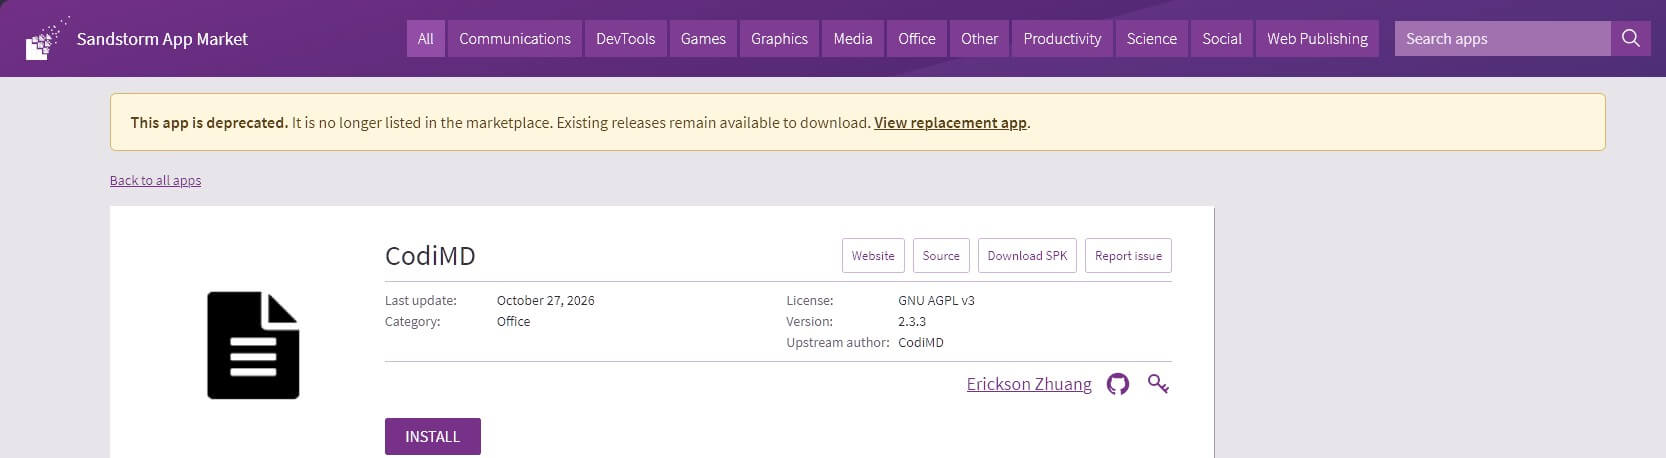
We used to advertise two versions of CodiMD, including one called SandMD, but now visiting both app pages will recommend you use HedgeDoc instead. The old apps remain installable in case you need the app to restore an old grain or complete a mass transfer.
Sandstorm apps are generally safe even if very outdated, so note that we will not deprecate apps because they are abandoned or old, deprecation is reserved for apps that have been fully replaced by a newer version.
A New Era for Sandstorm
By Jacob Weisz - 13 Oct 2026
tl;dr: We are announcing our first new release of Sandstorm, a fork of the previous startup’s code.
How we got here
Sandstorm has been code-frozen for over three years. The original startup closed, a core contributor of our project passed, and technical debt from the earliest days of Sandstorm reared its ugly head.
A longstanding problem for Sandstorm has been its use of MongoDB 2.6 as its underlying database. As Sandstorm uses an evergreen release model, all updates must be reliable and recoverable. Sandstorm servers have been deployed in diverse environments, making it challenging to build database migrations covering every scenario. For years, MongoDB 2.6 worked fine and work addressing this problem was deferred. Eventually, the Mongo driver for Meteor dropped support for MongoDB 2.6 and Sandstorm’s version of Meteor and its dependencies stagnated.
Additionally, Sandstorm has always been signed and released by Kenton Varda, the founder of Sandstorm. Every server operator who has installed Sandstorm has arguably placed their trust in Kenton. It does not make sense for Sandstorm servers to automatically install code Kenton has not reviewed and cannot personally vouch for.
As a project, we’ve decided to move forward as a fork of Sandstorm, where server operators make a deliberate decision to install our version of Sandstorm. This break in the update cadence also provides an opportunity: We can ensure administrators are actively involved in the process and can make a backup before the upgrade performs a database migration. With this plan in place, we looked for ways out of the project’s dependency-induced stagnation. At the same time, we started to spin up our own replacement infrastructure.
Recently, long-time contributor Michael Nutt, author of Davros and of Sandstorm’s WebDAV support, contributed a MongoDB migration, major dependency upgrades, and a variety of other tools and improvements. We’re ready to move forward with both updates and new features.
What to Expect
The latest Sandstorm build, 310, should be considered a release candidate. The visible changes in this release are few, but the underlying platform has substantial changes. There are upgrades to MongoDB, Meteor, and many package dependencies. We’ve replaced most references to sandstorm.io with sandstorm.org including the update sources and documentation. We believe it’s a solid, serviceable release, but many changes also create opportunities for problems.
We created new release signing keys and immediately released a second build to validate that the automatic update mechanism works as intended. However, until recently, all of this had been unused for many years. If you choose to update now, we recommend watching for updates in the event that manual action is required.
We’re releasing a migration script which should download, update, and migrate existing Sandstorm.io installations to our version. We strongly encourage you to have a full backup of your Sandstorm install before you proceed.
What’s Coming
Sandstorm has dependencies still in need of an update. After ensuring that the build is solid, we intend to continue updating the dependencies to the latest versions. Sandstorm also still uses Kenton’s app market and app index. We intend to replace those in the future.
We hope to support using passkeys as a login mechanism in a future release. We’re still interested in bringing Tempest to feature-parity with Sandstorm and beginning to direct our focus towards that in the future, but we’d like to ensure we can support the existing Sandstorm platform for the long-term as well. Separate from the core Sandstorm server, we’re working on updates, performance improvements, and bug fixes for many existing apps. We have new dev tools in progress to enable using Lima for cross-platorm app development, automatic app builds with GitHub Actions, and more.
The FAQ
Who am I trusting when I move to your fork?
The Sandstorm community project is currently led by Troy J. Farrell, Daniel Krol, and Jacob Weisz. All three of us have been involved in the Sandstorm community for many years, and have been continuously present in regular meetings for the past few years. You can chat with us on Zulip.
In June, we met in person for a key signing party, to verify each others’ identities and to create Sandstorm’s new release key.
Is Sandstorm developed with AI now?
Generally we consider ourselves to be skeptical of AI tools, but yes, AI development tools were a big part of building our way out of Sandstorm’s stagnation. For Sandstorm itself, we consider the use of AI-written code to be risky and review it very carefully. In the case of this upgrade, most of the code written with AI-assisted tools only occurs during the database migration. We need it to run once. The remaining code is largely the same code as before with newer dependencies.
We’re aware of the ethical and environmental concerns with generative AI, as well as the security and performance risks. As a small project with limited resources, we are taking advantage of the opportunity to keep the project alive and moving forward. We think Sandstorm’s usefulness for security and software independence outweigh the negative impacts of working with these tools in the short term.
Is Sandstorm still relevant in 2026?
Intriguingly, Sandstorm is in a unique position of being the ideal place to run “vibe-coded” applications: They’re aggressively sandboxed, and our goal of safely operating malicious apps means there are fewer security concerns when using AI tools to write Sandstorm apps.
In the last several years, many self-hosting platforms have been announced, but few isolate apps as well as Sandstorm does. Most are UI layers on top of normal Docker containers. Making apps work on Sandstorm requires more effort, but we believe the effort is worth the reward. We also believe that we can continue to make the process easier.
forSharingAccidentally: How Permissive Defaults and Unclear Documentation Cause Mistakes
By Jacob Weisz - 12 May 2025
tl;dr: We found a vulnerability in a few apps allowing unauthorized access to grains via API tokens. The last section has recommended actions.
We think of Sandstorm first and foremost as a security product. This means, in practice, we think of the security implications first, and the usability concerns second.
From time to time, when poking around our own project, we question the assumptions we make day-to-day. In this case, we decided to test a claim in the documentation, and it revealed an information-disclosure issue in multiple apps.
The problem
The issue in question is regarding Sandstorm’s use of “offer templates”, which are a way for apps to distribute API keys to users, often to connect client apps. Offer templates are a text template defined by the app which specifies how an API key will be shown to a user. The template, with the API key inserted, is then displayed by Sandstorm in an iframe. This approach is intended to prevent Sandstorm apps from reading their own API keys.
Offer templates are created by apps with some parameters. Sandstorm requires rpcId which identifies the template in case your app has multiple, and template which contains the actual template text. Several optional parameters are also available to describe the API key, style the template, and most critically set its authorization. roleAssignment restricts the key’s permissions by tying it to an app-defined “role”. forSharing determines whether the key meant to be given to someone other than the user, but what does this imply exactly?
In the documentation, it clearly states that if you use the forSharing option, the token in the offer template is detached from the user and can be reconfigured into a grain sharing link, in the format of https://SERVER/shared/TOKEN. This presents the natural assumption (and fatal mistake) that if you do not use forSharing, you cannot use the token in the form of a grain sharing link.
However, that assumption is incorrect. Regardless of the existence of the forSharing option, every API token works as a share token. Therefore, in the minimum offer template configuration, where neither roleAssignment nor forSharing is set, an API token can be used to access the full UI of the Sandstorm grain, at the same permissions as the user who created the token.
Another assumption which one might casually make, if API keys are just API keys, is that you can restrict the bounds of an API key using the app’s apiPath. This setting limits the root URL that an API call can make when used as an API key. But because the API tokens can be used to access the grain UI, that assumption is also perilous. API tokens are, fundamentally, granted capabilities, where knowing the resource also conveys the ability to use the resource.
Affected apps
In the case of most Sandstorm apps, this is actually not a significant issue: Users expect their client apps to have full access to their grains. For instance, a few apps use offer templates for Git clients and grant full access. This is okay because for these apps, each grain contains a single repository and full write access is expected. However, there’s a small category of Sandstorm apps where the token from the offer template is published publicly: Analytics tools.
We identified two analytics tools for Sandstorm which do not appropriately restrict access to the tracking token: Hummingbird and Sandstorm Error Collector. Notably, the Sandstorm Error Collector is used in the Sandstorm install script to allow people who fail to install Sandstorm to send the error code to us. It is possible to take the token from the installer script and use it to open the grain and see error reports. However, no user-identifying data is collected by this app.
Hummingbird is a website analytics tool. Anybody visiting a website that uses Hummingbird can view its source and obtain the API token. Hummingbird does define a “trackee” role, but for whatever reason the offer template did not end up using it for roleAssignment. As a result, it would be possible to use the API token to open the grain and watch analytics from currently active visitors to the site (not historical data). This includes location data which is obtained by the visitors’ IP addresses. While IP addresses are not directly exposed, the exposed location data could in theory be used to identify a “record” in the app’s GeoIP database which is associated with a set of possible IP addresses. The number of IP addresses in a record varies. More than 99% of IP addresses are in a record with 100 or more IP addresses. About 15,000 IP addresses are in a record with 10 or less. 911 IP addresses are in their own record, and could thus be identified uniquely by the visitor’s location. This is unfortunately non-zero exposure, but ultimately quite limited. (Daniel Krol did most of the investigation on the impact for this application.)
Additionally, the RMM app I am developing, XRF Sync, also should have used tokens with less permissive roles. However, in general different customers or tenants should be confined to their own grains, so the impact here is similarly limited.
Remediation and recommendations
We’ve patched all three vulnerable applications. (This section has been updated since initial publishing.)
Suggested actions for users: If you use these apps and are concerned about access to the grain, you should update your app(s), revoke your API tokens in the “webkey” menu, and create new tokens for your use.
We will update Sandstorm’s documentation to highlight that an API token can always be used to access the grain UI in the form of a sharing URL.
Critically for the future, we do not think security-critical properties should be optional. We’re going to move to start including roleAssignment in all offer templates, even when all permissions are expected, with a goal of making it a required configuration in Tempest. In the interim, app review will no longer accept submissions of packages which use offer templates without defining roleAssignment explicitly.
Getting On Zulip
By Daniel Krol - 29 Jan 2025
We are officially moving the chat portion of the Sandstorm Community to Zulip. Important announcements will go on our mailing lists, and you are still encouraged to continue to use them for questions if you prefer email over chat.
Zulip is an organized team chat app designed for efficient communication. It is built by a FOSS company which offers free hosting to FOSS projects such as ours. We appreciate this, and invite you to give them a look.
If you are still on Matrix, or especially if you are on IRC, we invite you to move over. Zulip will be a great way to collaborate at a faster pace than our mailing lists. You don’t need to install an app to join, though apps are available. You don’t even need to log in to see what’s happening.
A Little History
The Sandstorm project started out on IRC. This was long before the community fork. It was originally on Freenode, and eventually moved over to Libera.Chat as many others did.
We eventually bridged our Libera.Chat room to Matrix, allowing IRC and Matrix users to interoperate. Then in 2023, Libera.Chat decided to shut down their Matrix IRC bridge. First temporarily, then permanently. You can see comments on this topic from Matrix and Libera.Chat.
So now we had a split chat room, IRC and Matrix. By this time, most people had switched over to the Matrix side, which we decided to make the official one. It was still labeled as a sort of Libera.Chat “bridge to nowhere”, but we didn’t want to lose more people just to change our channel name. We did our best to let the few remaining IRC users know that the community moved over, though a handful people missed the message and stuck around.
But then, some time later, we were made aware of another problem: our channel was not allowing new members to join. We reached out to Matrix when we realized this, and we have yet to hear back. Perhaps moving to a new (non-bridge) Matrix room would fix it. But frankly, just as a personal preference, we were never in love with Matrix in the first place. If we were going to move, we were open to exploring new options.
More recently, one of our community members had been exposed to Zulip in a couple other open source communities. He suggested it for Sandstorm, so we tried it out. It’s a different animal than Matrix, but we ultimately decided that it would be a good fit for our community. We decided to make the switch!
Why Zulip?
Zulip conversations are organized into Channels and Topics. A Topic corresponds roughly to a “thread” in other chat apps, except that it is mandatory. That is, every post in a Channel has to be on a certain Topic. You can view a Channel as a whole or focus on a given Topic. This takes a little getting used to, but it keeps things organized.
If discussion in a thread starts to drift into a different subject, an admin can move those posts to a new appropriate Topic. Similarly Topics can be moved to a more appropriate Channel. This keeps us focused.
Channels can be made public and searchable on the web, and we have made most of our channels public. Specific conversations are linkable (such as the link in the paragraph below). As with mailing lists, this is very useful for an open source project. For instance, a Github pull request can link to where the idea was previously hashed out on Zulip.
Not to mention, Zulip is just snappy. It’s not bulky like Slack or Matrix. We find all these features conducive to having productive conversations. This is where we can “get in the weeds” and work things out.
They’re also great to work with. They responded and resolved a bug report overnight. (Again, by contrast we reached out to Matrix for help with the bridge and we never heard back).
Sandstorm now belongs to Sandstorm.org
By Kenton Varda - 14 Jan 2024
TL;DR: Primary maintainership of the Sandstorm project has changed, and a along with that, the project has moved to sandstorm.org.
The “New” Sandstorm Project
I’ll start with the point: I, Kenton Varda, am no longer the maintainer of the Sandstorm project. In fact, I haven’t really been for quite some time. Instead, a group of avid Sandstorm users, led by Jacob “ocdtrekkie” Weisz, have been doing a lot more work than me. Many have been involved for quite a few years now.
Yet until recently I have continued to hold the role of gatekeeper: I was the one who could push releases, merge changes, approve blog posts, etc., but was failing to do so. That doesn’t make sense.
So, I’m relinquishing that control. Sandstorm now belongs to the Sandstorm Community under Open Source Collective.
However, Jake and I agree that this change should be very explicit. People coming to the Sandstorm web site today are often confused about Sandstorm’s status, even thinking it is backed by a company – we need to make things clear. And, it doesn’t necessarily make sense for for people who who opted into auto-updates back when Sandstorm was a company to keep getting them from the community. Not only because those users may not be comfortable with it, but also because the community itself may not be. Sandstorm’s users included (and may still include – there’s no way for us to tell) companies, newspapers, educational institutions, research laboratories, and even government agencies. An auto-update that, say, breaks SAML login could do a lot of damage overnight. For the community to make progress, the stakes need to be a little lower.
To that end, the new project is going to live under a new domain, sandstorm.org. Hopefully, the .org TLD, along with some design changes, makes it clear that this is a community project, not a company. sandstorm.io will stay as it is, but with the banner you see above flagging it as historical. If and when sandstorm.org decides to push auto-updates, users will have to manually opt into them.
For my part, I continue to be a Sandstorm user, and as a user I do hope the project is able to make progress under new maintainership. Time will tell.
Sandstorm’s Backstory
For those curious how we got here, here’s the whole story from the beginning…
Long ago – circa 2014 to 2016 – Sandstorm was a startup, of which I was co-founder. We ran a successful crowdfunding campaign in 2014 and raised VC money in early 2015. We hired 5 people, making a team of 7. We had aimed for a series A round in 2016. We saw a lot of developer excitement for our product on Hacker News and the like, and we expected to follow in the footsteps of other startups who were able to raise a pre-revenue series A based on such excitement. Unfortunately, that did not happen. For whatever reason – and I could list several possible reasons, but I’ll never really know which it was – investors weren’t interested. This set off a panic where we lowered our sights to raising a “bridge round” while trying to produce actual revenue from enterprise sales. But this made things worse: we did not have any idea how enterprise sales worked. We made two sales ever, for a measly 4 figures. Investors ran away.
By the end of 2016, it was obvious the company was going to crash, so we started looking for an acquisition. Too late, of course – our potential acquirers knew it was a fire sale. There was a common saying in Silicon Valley startup circles at the time that in a pure acquihire, your company is worth $1M per engineer. We learned quickly what should have been obvious: this is a fanciful myth. You cannot block another company from hiring your employees, so why on Earth would they pay you – or rather, your investors – for the right? Just to be nice? Several companies were very interested in our engineers, but the best they offered was to acquire the company for $0 and help us wind it down, while making job offers to some or all of the employees.
One company (whom I won’t name, but you’ve heard of) actually told us: “We will add up all the salaries and stock grants we offer your employees, and that’s what you can say was the exit price. If you’d like, you can take a chunk of the equity and give it to your investors rather than the employees.” I found this extremely disturbing. Another company (you’ve heard of them too) interviewed the whole team and then informed us they were passing on the founders but hiring two employees.
Another company we talked to was Cloudflare. They too offered to acquire the company for $0, but they made good offers to the whole team without any funny business. Additionally, they had a project in mind for me. They said: “We know we want to let people run code on our edge network, but we haven’t figured out exactly how. We could give you ownership of this.” I was intrigued. And after paying myself $60k/year for several years, boy did that regular salary look nice.
But I still very much wanted Sandstorm to succeed. So I told Cloudflare, I’ll come work for you, but I want to keep Sandstorm the company, and be able to work on it as an open source project. They agreed.
So in early 2017 we announced that Sandstorm was moving to a community model and, shortly after, that most of the team joined Cloudflare.
For some time, I continued to work actively on Sandstorm, and a motley crew of community members helped out. But at the same time, by day, I was having the most fun of my career, having been given a greenfield project to hack on with no distractions. That project became Cloudflare Workers. Within six months we released a beta, and (coincidentally) exactly a year after I joined Cloudflare, we officially launched the product. The product has continued to grow on a startup-like trajectory ever since.
So, I was (and am) now essentially the founder of a startup-within-Cloudflare which was actually succeeding. It became hard to put energy into Sandstorm, the project that felt like a failure, even if I still believed in it. Sandstorm became increasingly a chore: Once a month I would review and merge pull requests, update dependencies, and push a new build. If I spent time on it beyond that, it was to shut down the paid hosting service (which never had enough users to make money) or switch sandcats.io to Let’s Encrypt when our previous contract with Globalsign expired.
Over time, even just basic maintenance became difficult. Sandstorm uses MongoDB for metadata storage, but it is stuck on version 2.6, which is ancient. I couldn’t update it because updating Mongo requires manual intervention, but Sandstorm is something that thousands of users have installed and expect to auto-update. Most of them aren’t even aware they are running Mongo. Maybe I could have written code that would automatically handle the migration? That sounded like more work than I was interested in. Eventually, though, the Mongo drivers used by Meteor were updated to a version that didn’t support 2.6. So now I couldn’t update Meteor, Sandstorm’s primary dependency. And we can’t update Node, because old Meteor doesn’t work on newer Node. (That, by the way, is largely because V8 made a change which permanently broke node-fibers, which Meteor deeply depended on. Oh the tangled web we weave…)
During all this time, the Sandstorm web site remained mostly unchanged, save for the occasional blog post. I think this has been misleading. The site was designed when Sandstorm was a company, by our full-time professional designer. We made some changes after the company shut down, but it still looks like a company’s web site. People seem to stumble across the page and believe it is backed by a full-time team rather than a few volunteers. From time to time it even shows up on the front page of Hacker News.
I have felt bad about this, but couldn’t quite figure out what to do. Redesign the web site to make it look less professional? I’m not quite sure even how to do that, but I’m pretty sure I don’t have time.
In late 2022, the one person who had been contributing code changes to Sandstorm with some regularity, Ian “zenhack” Denhardt, decided to embark on a total rewrite called Tempest, so contributions to the main project dried up. In early 2023, I gave up pushing monthly releases, since there seemed to be no point: no code changes had been made and no dependencies could be updated.
And then in mid-2023, tragically, Ian passed away in an accident. I’m no good at eulogies, but suffice to say it was a big loss for Sandstorm, Cap’n Proto, and other communities Ian was in.
Later in 2023, Jake wrote a blog post, originally to be posted on sandstorm.io, requiring my approval. The post was ambitious, and even though I wasn’t being asked to do anything except approve it, I felt that doing so implied a commitment on my part that I wasn’t prepared to make. Instead, we made the decision that I should take myself out of the loop. We came up with the plan to transfer leadership of the project. Sandstorm-the-company had long owned the domain sandstorm.org but not used it; I decided it made sense for this to become the new home of the community project and transferred it to them.
For reasons I can’t go into here, I was unable to dissolve Sandstorm the company until some time in 2022. (It turns out I really should have accepted the $0 offer from Cloudflare, to make it their problem, but alas.) But once I could finally do it, our investors and I agreed on a dissolution plan that allowed Sandstorm’s remaining IP to be transferred to a non-profit entity representing the community. Of course, the code is open source under the Apache license, so anyone can freely use that. But, the agreement also covers trademarks, domain names, etc. Open Source Collective is a qualifying non-profit.
And so, here we are. Sandstorm now belongs to Sandstorm.org.